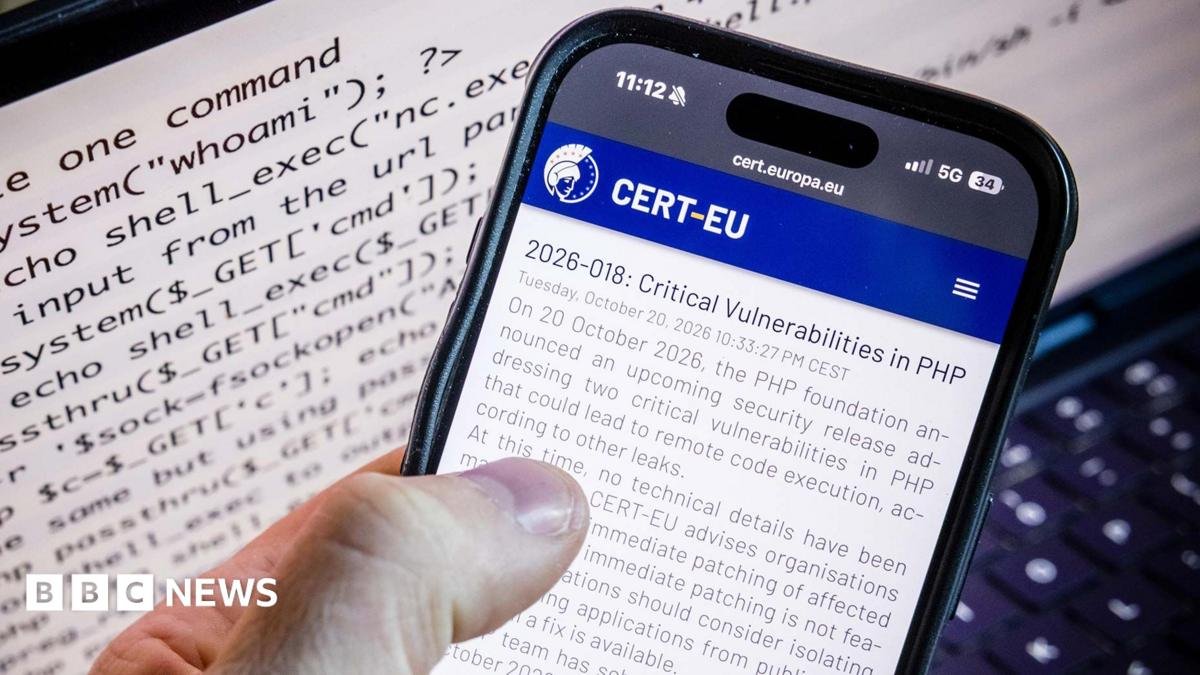
The PHP flaws were initially found by humans back in 2024, Woodward tells Radio 4’s Today programme, but they thought it looked “too complicated to exploit”.
As large language models – a type of artificial intelligence (AI) – became more sophisticated, “people worked out how to exploit [the flaw]”, the cyber security professor says.
“People have been scrambling away saying: ‘Actually, yes, you can exploit it and we now need to patch it’,” Woodward explains.
Part of the problem is that “the cat was let out of the bag rather earlier than it was supposed to have been,” he says, adding that somebody revealed the PHP flaws before the patch – an update to fix the issue – was made public.
Asked whether it has led to hacking attempts, Woodward says companies like Amazon and Cloudflare that monitor what is going on online saw the weakness “was being probed for”.
He adds: “We don’t know whether [sites have] been attacked but certainly people were probing websites to see: have you got that flaw?”