Researchers used Claude to breach OpenAI’s internal systems
Researchers from security firm Hacktron said they found a security flaw in OpenAI’s public help forum that allowed them to take control of the site.
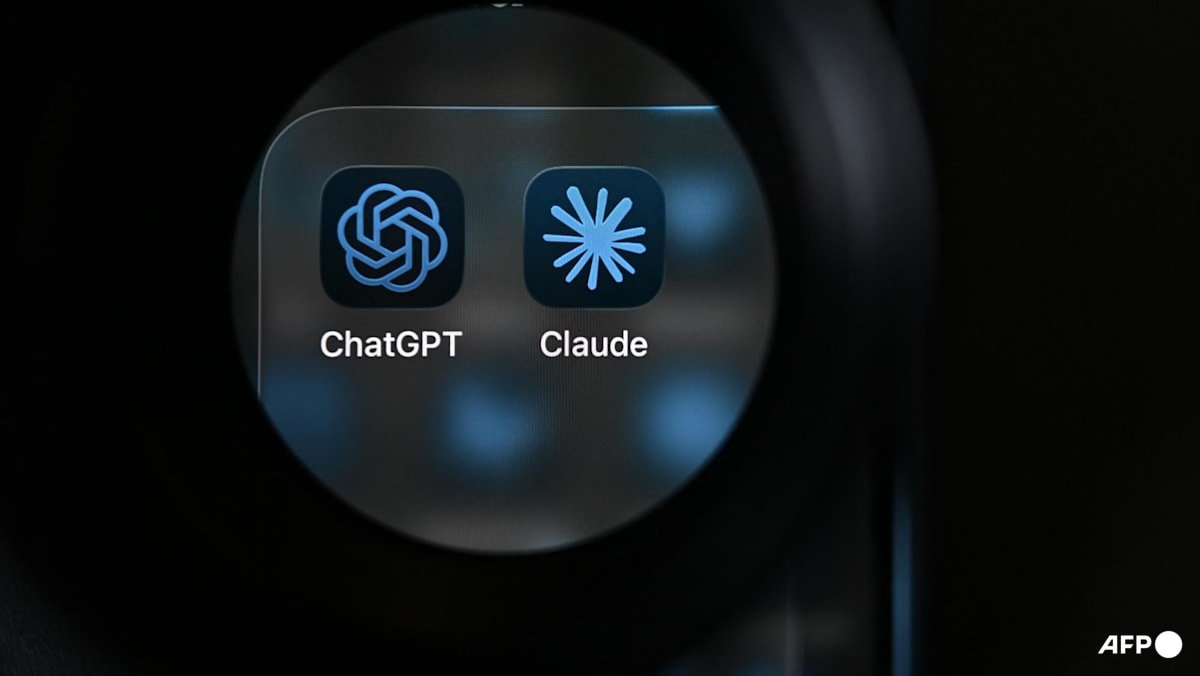
The app logos of artificial intelligence (AI) assistants ChatGPT by US Company OpenAI and Claude by US AI safety and research company Anthropic displayed on a smartphone’s screen, in Brussels on Jun 10, 2026. (File photo: AFP/Nicolas Tucat)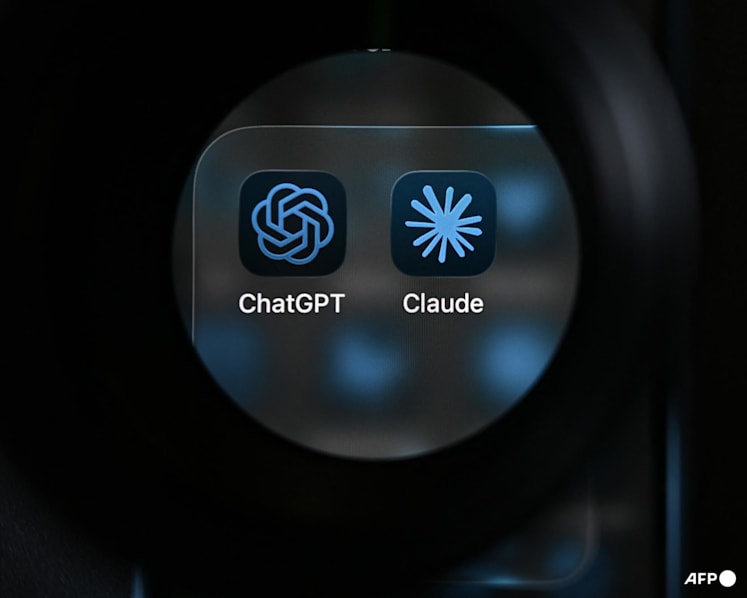
Read a summary of this article on FAST.
Get bite-sized news via a new
cards interface. Give it a try.
Click here to return to FAST
Tap here to return to FAST
FAST
WASHINGTON: A security research company said on Friday (Sep 18) it managed to break into OpenAI’s internal systems using the latest software from Anthropic, exposing how quickly the technology can carry out sophisticated cyberattacks.
The researchers from security firm Hacktron said they found a security flaw in OpenAI’s public help forum, run by the Discourse platform, that allowed them to take control of the site.
“We immediately reported the initial vulnerability to OpenAI and Discourse and worked with them to coordinate the patch,” Hacktron said in a blog post.
“We appreciate their attention to detail and fast resolution of this issue,” the post added.
Guess Word
Crack the word, one row at a time
Buzzword
Create words using the given letters
Mini Sudoku
Tiny puzzle, mighty brain teaser
Mini Crossword
Small grid, big challenge
Word Search
Spot as many words as you can
OpenAI confirmed the flaw was fixed within about 14 hours of being notified and paid the researchers a US$6,500 reward.
“We thank the researchers for contacting us and sharing their findings. We narrowed the permissions on Community sign-in tokens and revoked affected tokens and sessions,” said Drew Pusateri, an OpenAI spokesperson.
The Hacktron researchers said they initially used Anthropic’s Claude Opus 4.8 to identify and exploit the software flaw, but struggled to make it work consistently.
After Anthropic released Claude Opus 5, the researchers said the newer model produced a working hack within about three hours.
The hackers did not use Claude Mythos, a more capable Anthropic model that is restricted to a small group of vetted cyber-defense organisations.
Anthropic has described Mythos as having the strongest cybersecurity capabilities of any model it has built.
Hacktron said the underlying software flaw is not unique to OpenAI and is used across many companies’ products, including those made by Slack and Meta.
The firm said it is continuing similar tests at other companies.
The case adds to growing concern among security experts that AI tools are making it faster and cheaper to carry out sophisticated cyberattacks that once required specialised teams and months of work.

Source: AFP/dy
Sign up for our newsletters
Get the CNA app
Stay updated with notifications for breaking news and our best stories
Get WhatsApp alerts
Join our channel for the top reads for the day on your preferred chat app
Get bite-sized news via a new
cards interface. Give it a try.
Click here to return to FAST
Tap here to return to FAST
FAST