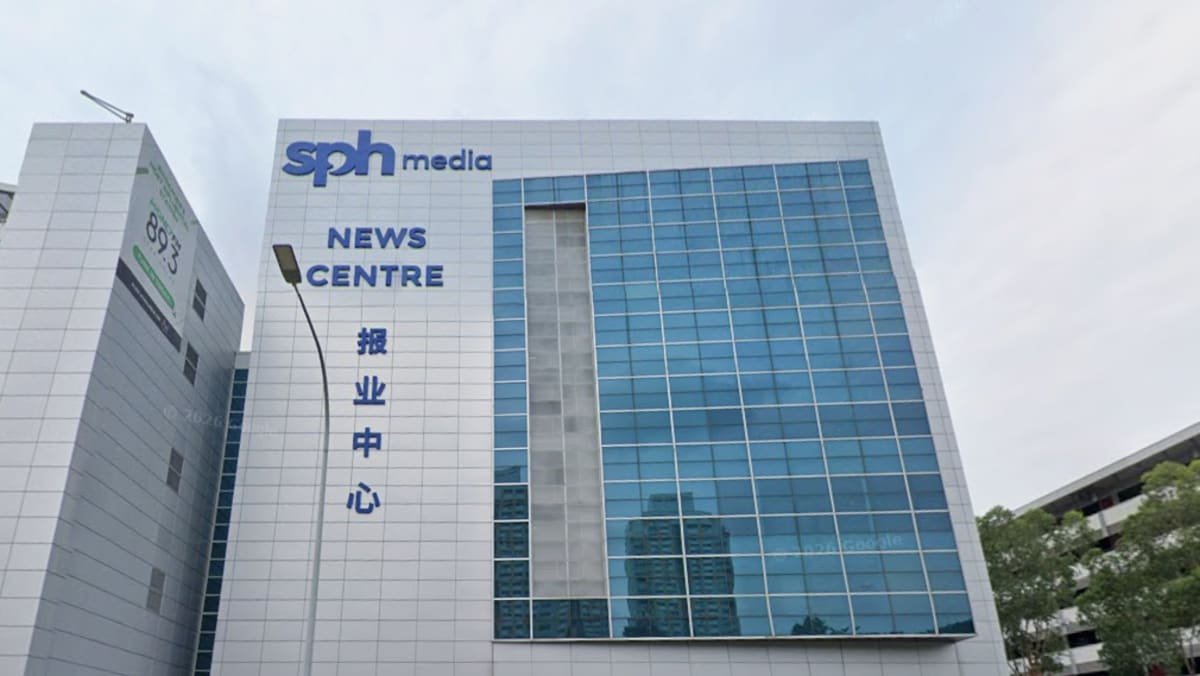
SPH Media hit by cyberattacks; says no customer financial data or access exposed
The cyberattacks were believed to be a concerted effort by the same threat actor, an SPH Media spokesperson said.
A view of the SPH Media building. (Image: Google Maps)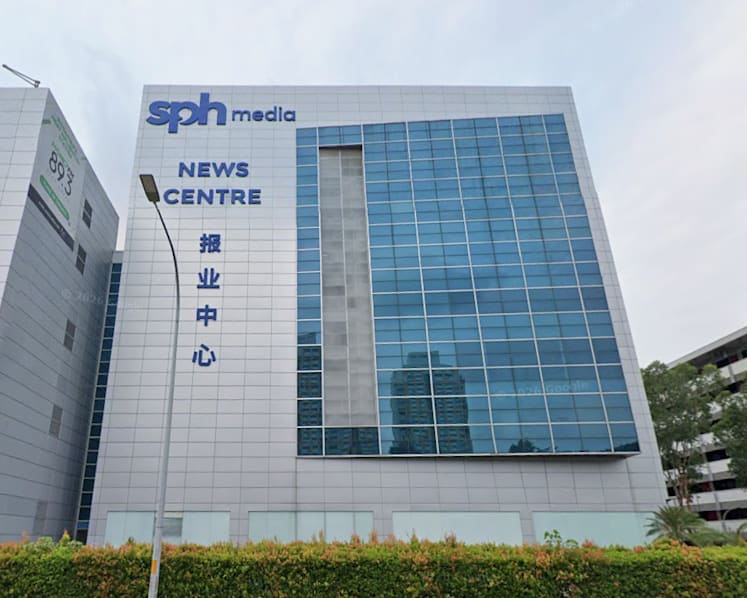
New: You can now listen to articles.

This audio is generated by an AI tool.
Read a summary of this article on FAST.
Get bite-sized news via a new
cards interface. Give it a try.
Click here to return to FAST
Tap here to return to FAST
FAST
SINGAPORE: SPH Media has been hit by cyberattacks on five of its systems, but no customer financial information or account access was compromised, the company said on Tuesday (Nov 10).
“(The cyberattacks) are believed to be a concerted effort that was carried out by the same threat actor,” an SPH Media spokesperson said in response to CNA’s queries, without elaborating on the nature of the threat actor.
The cyberattacks hit two groups of SPH Media’s systems: one on systems that contained some personal data, and the other on systems that did not store any such data.
The compromised information included mostly email addresses, names, mailing addresses and phone numbers. This amounted to 9 per cent of the company’s database.
“No payment card details, financial or banking information, or customer account access was compromised,” said the spokesperson.
Guess Word
Crack the word, one row at a time
Buzzword
Create words using the given letters
Mini Sudoku
Tiny puzzle, mighty brain teaser
Mini Crossword
Small grid, big challenge
Word Search
Spot as many words as you can
The SPH Media statement did not specify the extent of its database exposed by the cyberattacks that hit systems not containing personal data.
“Upon discovering the incidents, we immediately took steps to secure the affected systems and engaged external cybersecurity experts to investigate and contain the breaches.”
SPH Media said that it also reported the incident to the Personal Data Protection Commission (PDPC), the Cyber Security Agency of Singapore (CSA), the Infocomm Media Development Authority (IMDA) and the police.
It added that it informed all affected parties about the incident and advised them about the precautions to take.
“SPH Media takes the security and confidentiality of customers’ information very seriously, and has been working very closely with the relevant authorities and third-party specialists.”
The Straits Times, which is owned by SPH Media, reported that the first cyberattack incident was detected on Nov 4, and the most recent incident on Nov 8. The SPH Media spokesperson declined to confirm the dates.
CNA has contacted the PDPC, which is under IMDA, and the CSA for more information.
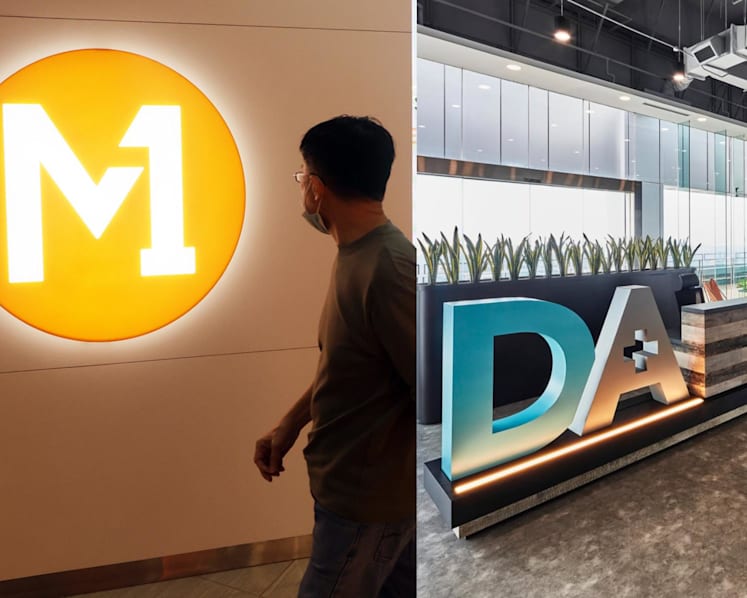
The incident follows other reported data breaches, including those involving telco M1 and telehealth provider Doctor Anywhere on Nov 6.
The M1 data breach exposed customers’ personal information, including names, NRIC or FIN numbers, dates of birth, mobile numbers, email addresses and residential addresses.
Doctor Anywhere also reported a leak of users’ personal data, although cybersecurity and forensic specialist Ensign InfoSecurity said clinical records were not affected.
Separately, data relating to around 46,000 Singapore Airlines booking records was accessed in a breach involving software provider Amadeus, which affected at least eight airlines.

Source: CNA/rk/dy/(gf)
Sign up for our newsletters
Get the CNA app
Stay updated with notifications for breaking news and our best stories
Get WhatsApp alerts
Join our channel for the top reads for the day on your preferred chat app
Get bite-sized news via a new
cards interface. Give it a try.
Click here to return to FAST
Tap here to return to FAST
FAST